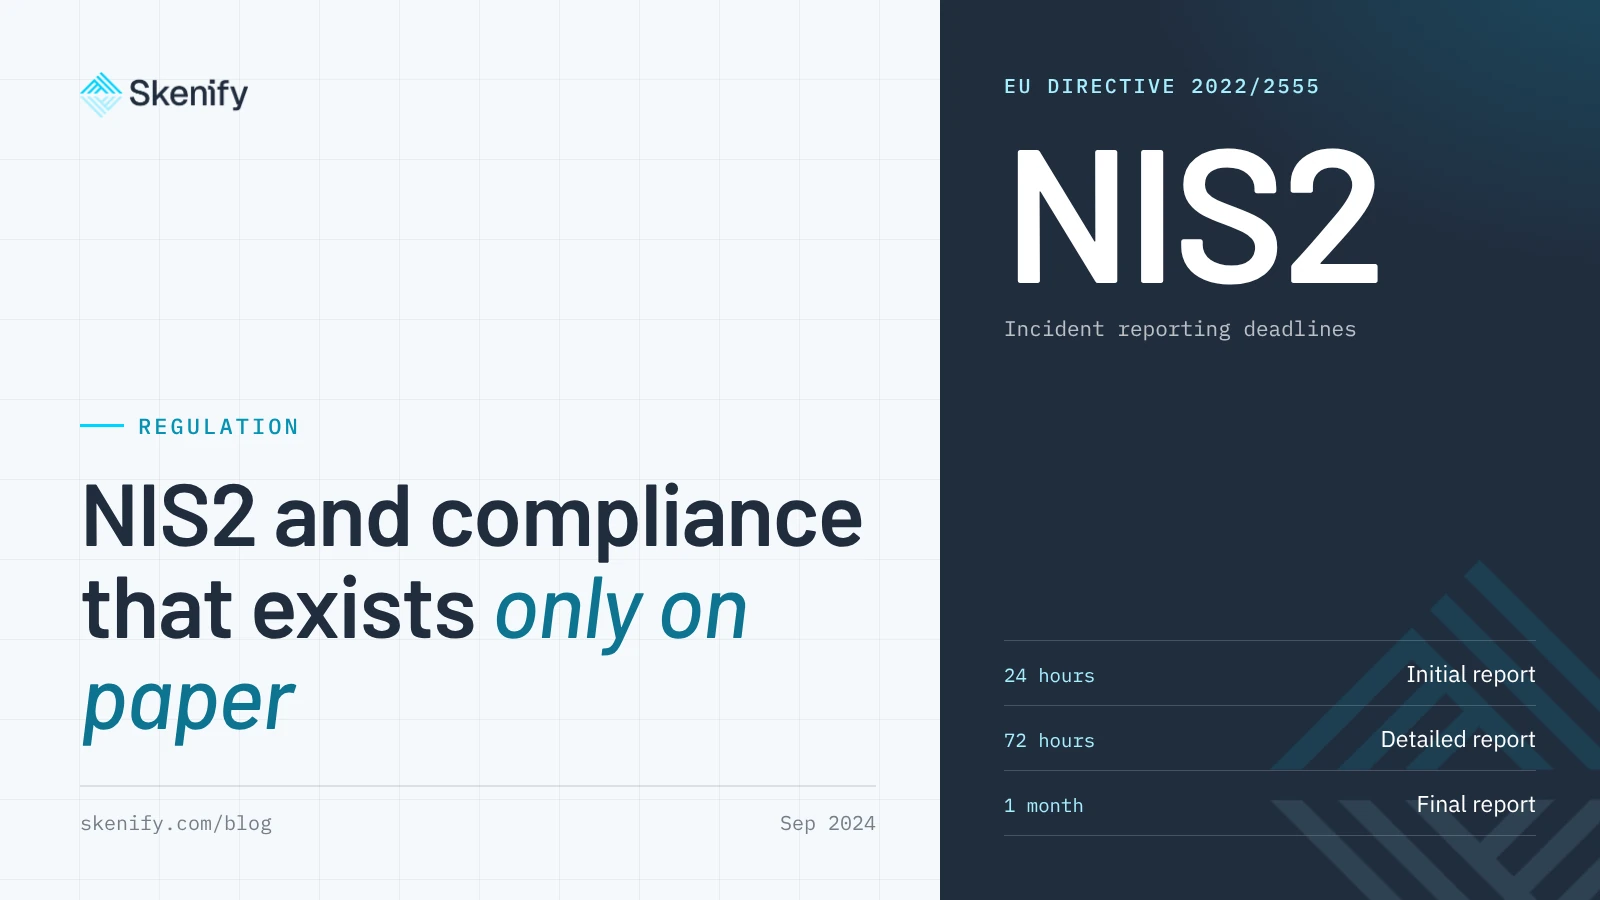
NIS2 is the EU directive on cybersecurity for essential and important entities. Member states had to transpose it by 17 October 2024. It applies to medium and large organisations in sectors such as energy, transport, banking, healthcare, digital infrastructure, managed ICT services, manufacturing and food production. It also reaches smaller suppliers, because covered entities have to manage the security of their supply chain.
What is at stake
- Essential entities: fines of up to 10 million EUR or 2% of global annual turnover.
- Important entities: fines of up to 7 million EUR or 1.4% of global annual turnover.
- Incident reporting: an early warning within 24 hours and a notification within 72 hours.
- Management: the management body approves the measures and can be held liable.
The ten measures of Article 21(2)
Skenify does not make you compliant on its own, and no tool does. It produces the technical evidence for the measures a platform can observe from the outside and from your Google Workspace or Microsoft 365 tenant. Policies, contracts and internal procedures remain yours. The list below shows the split for each measure.
- (a) Risk analysis and security policies. Skenify keeps a risk register with inherent and residual scoring, mapped to ISO 27001 controls. The policies are yours.
- (b) Incident handling. Early warnings show compromised accounts, leaked credentials and exposure changes before they become incidents, and the register records ownership and timelines. Classification and reporting to the authority are yours.
- (c) Business continuity. Continuity risks are recorded in the register and mapped to controls. The continuity and recovery plans are yours.
- (d) Supply chain security. Skenify discovers the third-party apps your people authorised, with their permissions, risk score and reach. Supplier policies and contracts are yours.
- (e) Security of systems, including vulnerability handling. Findings are confirmed on the live asset, with CVSS, impact and the fix. Acquisition, development and disclosure processes are yours.
- (f) Assessing effectiveness. Expert penetration tests are requested in the platform and the reports serve as testing evidence.
- (g) Cyber hygiene and training. Awareness training is on our roadmap. Today, breached credentials and email security checks identify exposures.
- (h) Cryptography. Certificates and TLS configuration are monitored on every host. The cryptography policy is yours.
- (i) Human resources security and access control. Tenant accounts and authorised third-party apps are listed with permission risk and reach. HR and access policies are yours.
- (j) Multi-factor authentication. Skenify shows breached credentials and third-party access. Enforcing MFA is yours.
Where to start this week
- Take the free NIS2 gap assessment. It takes about five minutes, shows your score at once and sends the gap report to your email.
- Work through the security checklist of 46 practices, which is mapped to NIS2 and DORA and available as a free PDF.
- If your company operates in Montenegro, read our guide to the Zakon o informacionoj bezbjednosti, which transposes these obligations into national law.
Sources
Legal textEUR-Lex14 Dec 2022
Directive (EU) 2022/2555 (NIS2)
On Skenify
Check your gaps against NIS2 in five minutes. Your score is shown at once.
Take the free NIS2 gap assessment