
01Connect
Sign in with Google or Microsoft. Your domain comes from your email address and the first assessment starts. Connect the workspace and discovery extends to accounts and third-party apps.
Connect
skenify.comDomain verified
Microsoft 365
Attack surface and risk management for companies without a security team
Skenify finds everything your company exposes on the internet and tests it. Each finding is confirmed on the live asset before it reaches you, so your list holds no false positives. You get tasks ranked for your business, each with the exact change to make and a deadline.
Seven days, no card. Requests are approved within 24 hours. First findings fifteen minutes after you connect.
1 domain, 5 hosts, 20 ports, 3 certificates
ISO 27001 certified
ISO 42001 certified
Data in Frankfurt, EU
Founded by a CISO
Track record
From our team's penetration testing work through The Security Company, 2021 to November 2026. Anonymised.
See the data

A staging host nobody documented. A vendor your finance team authorised in 2023. A password in a breach dump from a service nobody remembers. This is how small companies get breached, and none of it stands out in a scanner report with four hundred rows. Skenify looks at your company the way an attacker does, then tells you the three things to fix this week.
A customer questionnaire, an insurance form or a regulator wants evidence. Skenify answers with a score, a report and a record of what you fixed and when.
See the reportsYou keep the company running and security is one more thing on the list. Skenify hands you tasks with the exact change to make, in the order that reduces risk fastest.
See the task boardEvery client behind one login, each with its own workspace, register and board. You get margin, a product that does the delivery, and a story your clients understand.
Partner programmeWhat happens to a single weakness in Skenify, from the moment you connect to the moment it is closed.
Sign in with Google or Microsoft. Your domain comes from your email address and the first assessment starts. Connect the workspace and discovery extends to accounts and third-party apps.
Skenify walks outward from the domain: 15 subdomains, 8 hosts, 35 open ports, every certificate and DNS record. Nothing to type in, nothing to install.
| skenify.com | Domain | 0 ports | 12 found |
| app.skenify.com | Host | 2 ports | |
| api.skenify.com | Host | 13 ports | |
| auth.skenify.com | Host | 13 ports | |
| backoffice.skenify.com | Host | 2 ports | |
| dev.skenify.com | Host | 2 ports |
Each asset gets the checks that fit it. The web application scan finds that app.skenify.com runs an unpatched web server with a known remote code execution flaw. Confirmed on the live host before it reaches your list, scored 9.8, explained in plain language.
app.skenify.com CVSS 9.8
The server version is affected by a published path traversal and code execution flaw. An unauthenticated attacker can run commands on the host.
The finding becomes risk R-01: an unpatched web server allows attackers to run code on the host and reach customer data. Skenify scores it with your business context: inherent score 20, residual 4 once treated. ISO 27001 controls A.8.8 and A.8.9 attach themselves.
Inherent
20
CriticalResidual
4
LowA task lands on the board: update the web server to the patched release, with the exact commands and a 7 day deadline from the SLA. Someone on your team takes it. When they close it, the risk drops and the score climbs.
apt install --only-upgrade apache2 && systemctl restart apache2 && curl -sI app.skenify.com | grep Server
 Due in 7 daysCritical
Every closed task moves the score. This is what 90 days of the chain look like.
+22 points
Score improvement
41 tasks closed
In 90 days
0 past SLA
Tasks overdue
Skenify builds a business context for your company from the public web and from your own environment, and keeps it current. That context decides how each finding is scored, which risk it becomes and what the task says.
acme.io
Business context
No generic findings. No generic risks. No false positives.
Six views of the same register. Each one feeds the next.
Every domain, subdomain, IP, port and certificate, redrawn as your footprint changes. List or graph.
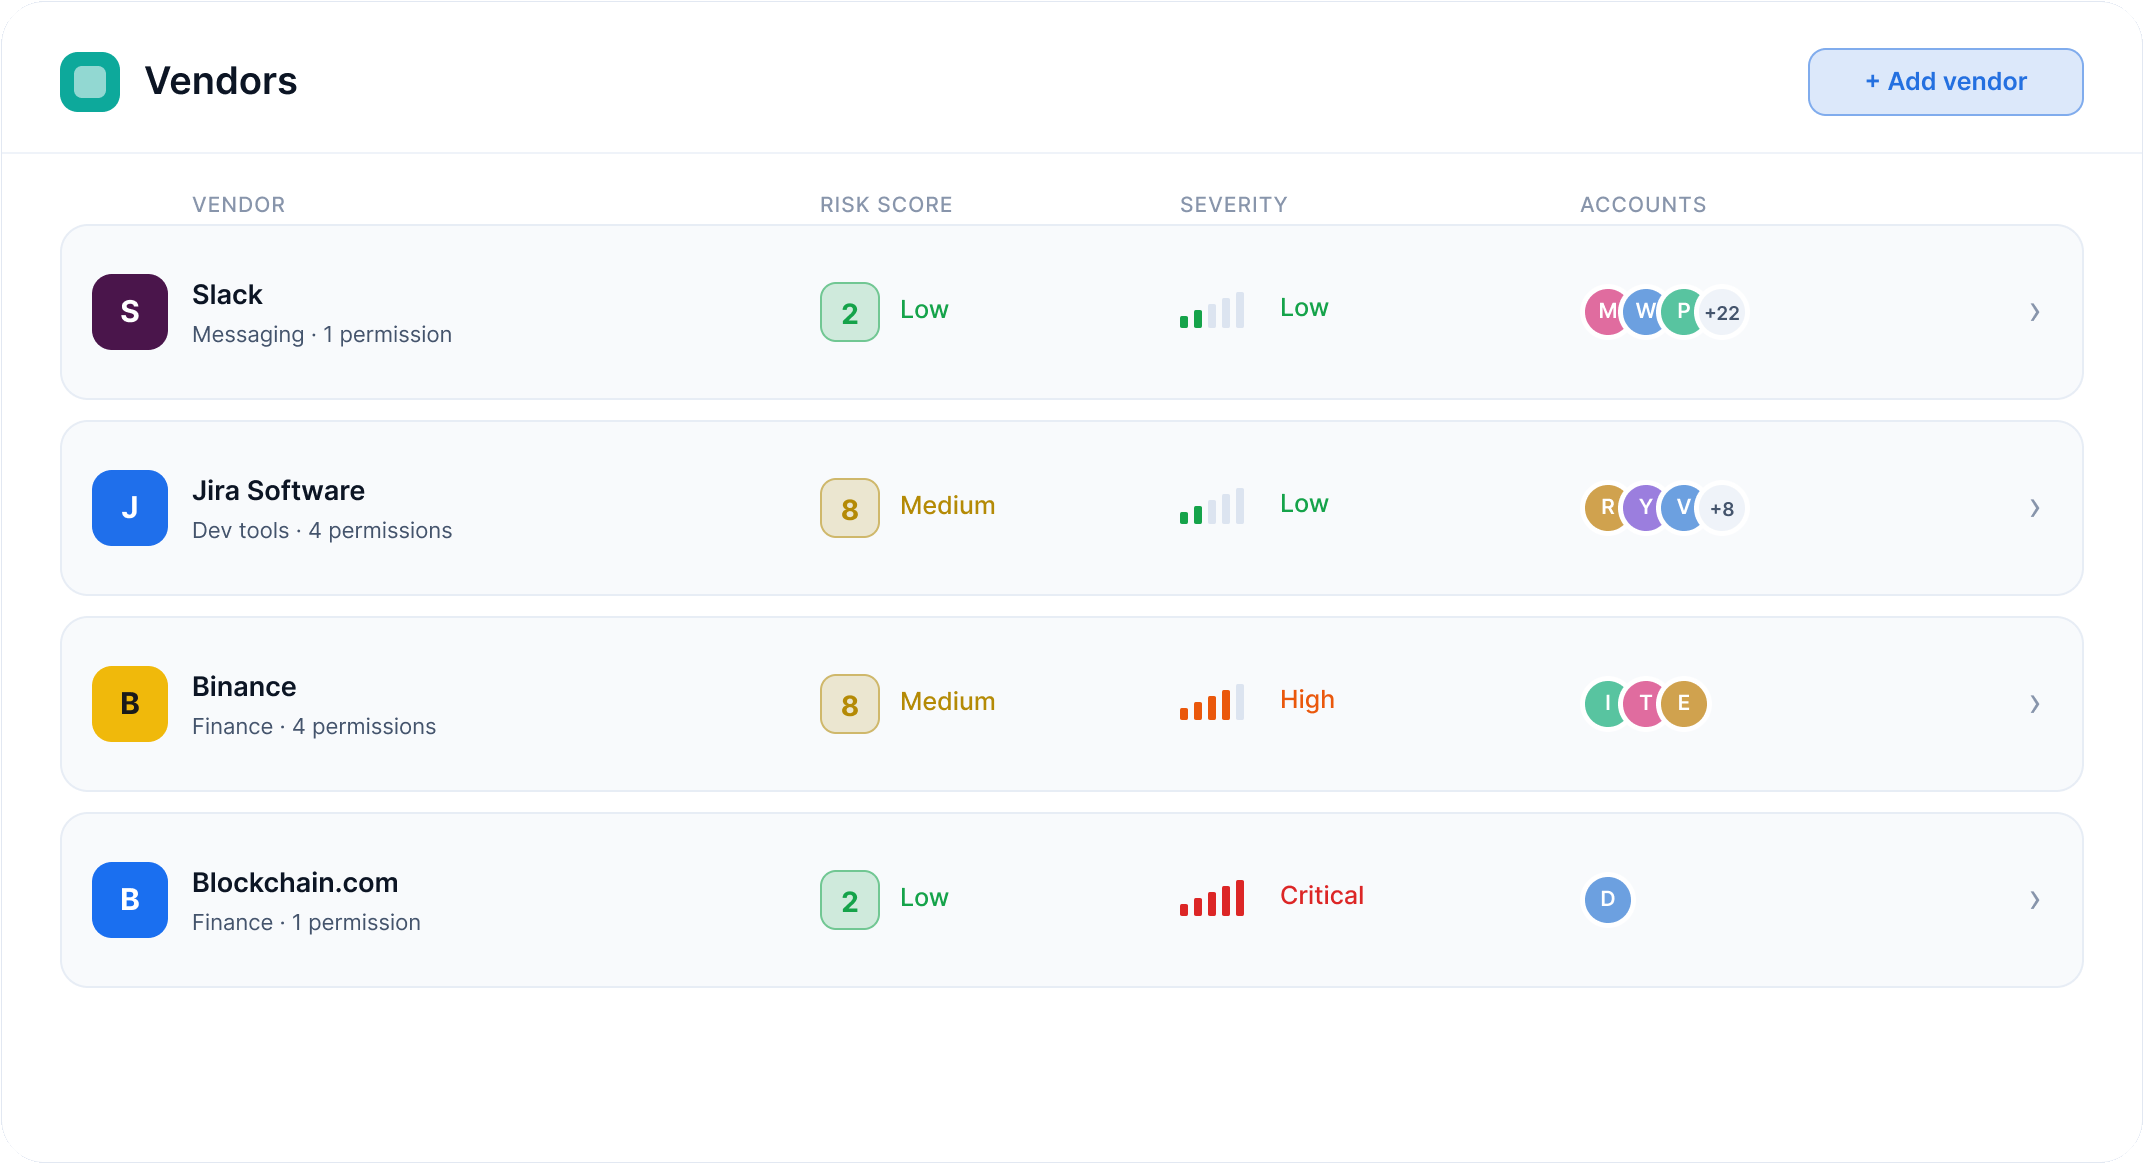
The third-party apps your people authorised, with the permissions each one holds and how far it reaches.
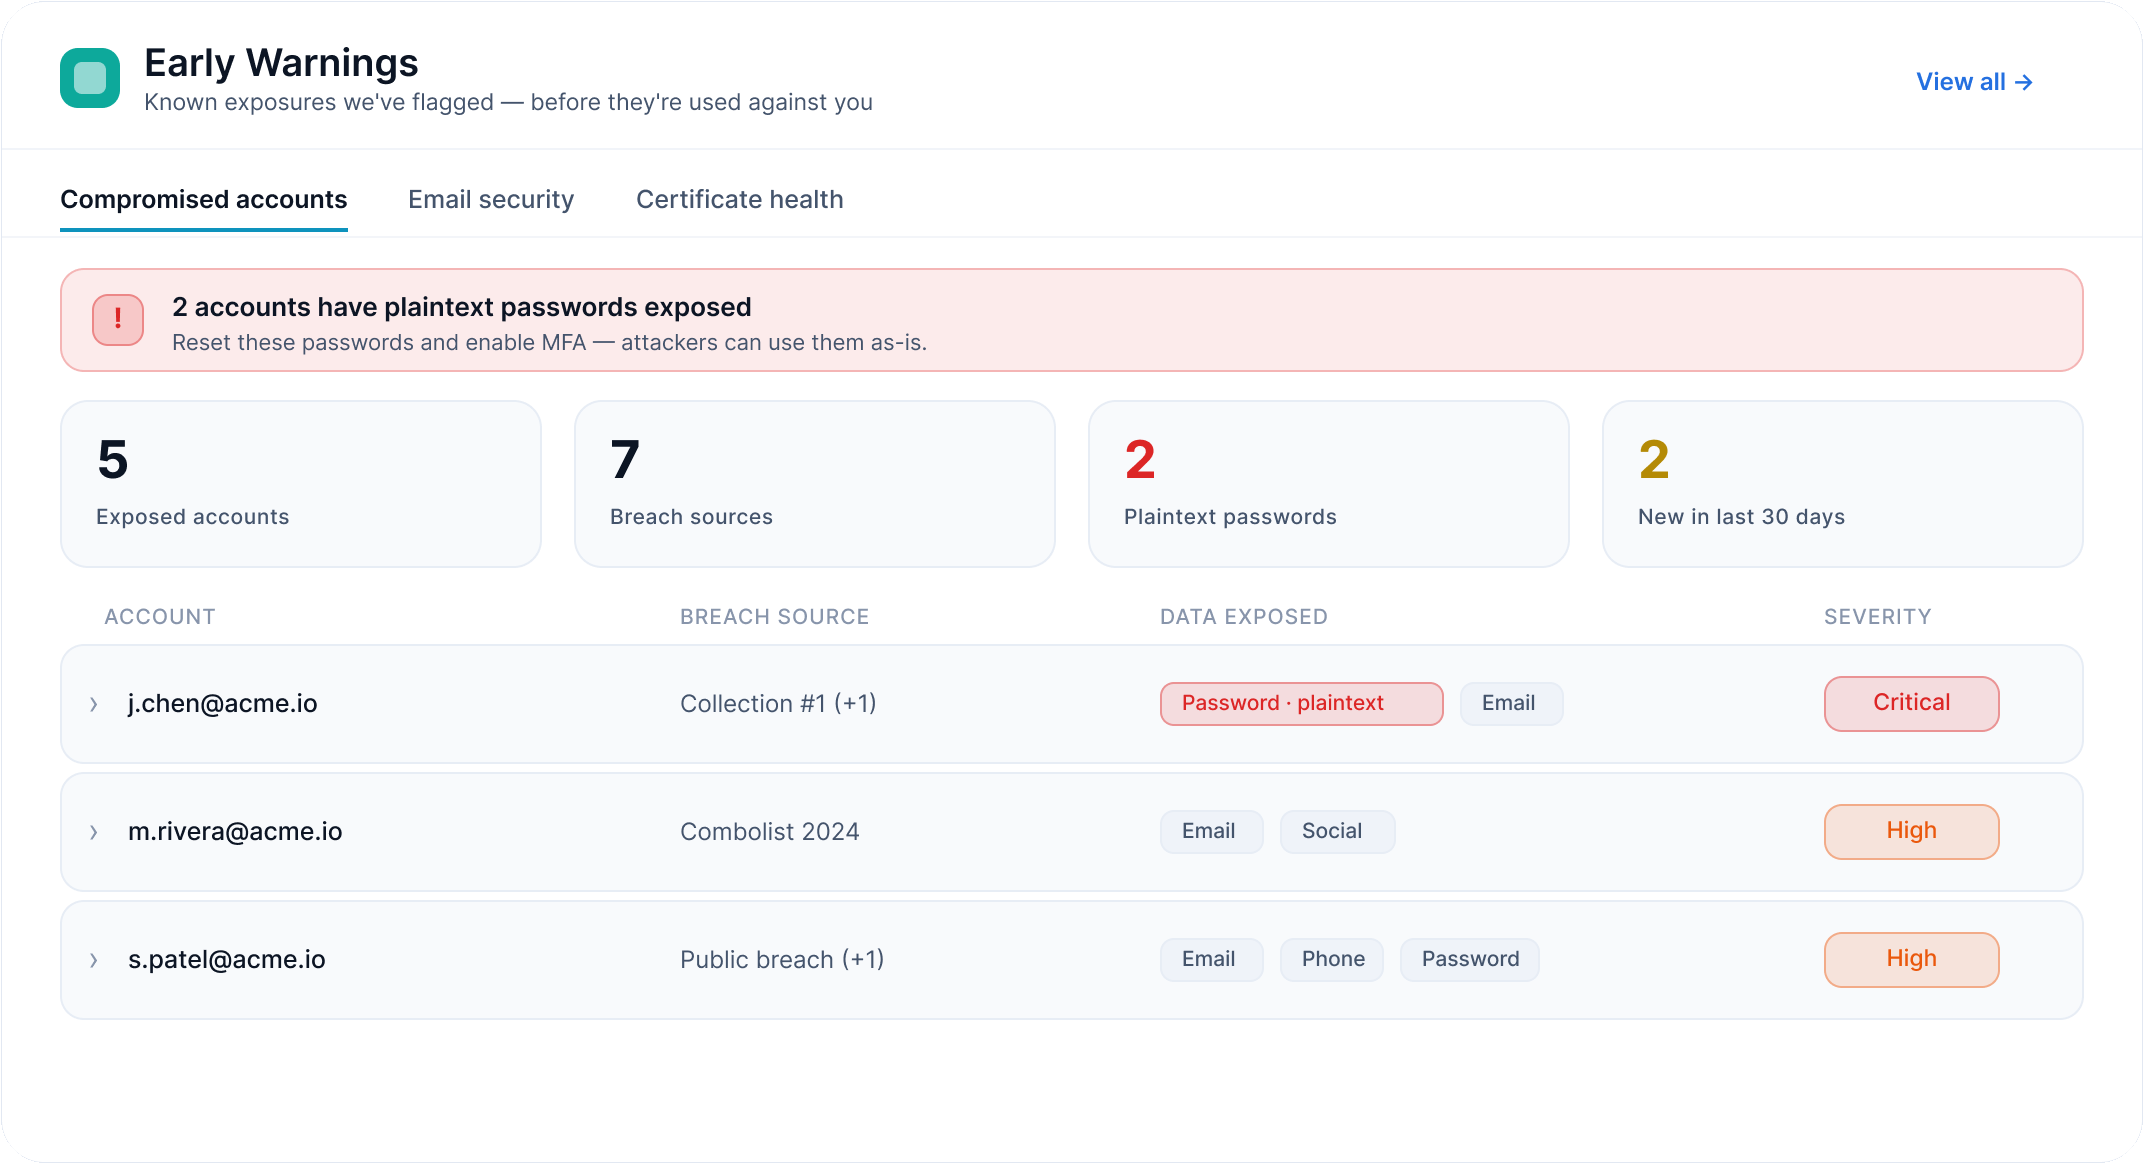
Breached credentials, spoofable domains and expiring certificates, flagged before someone uses them.
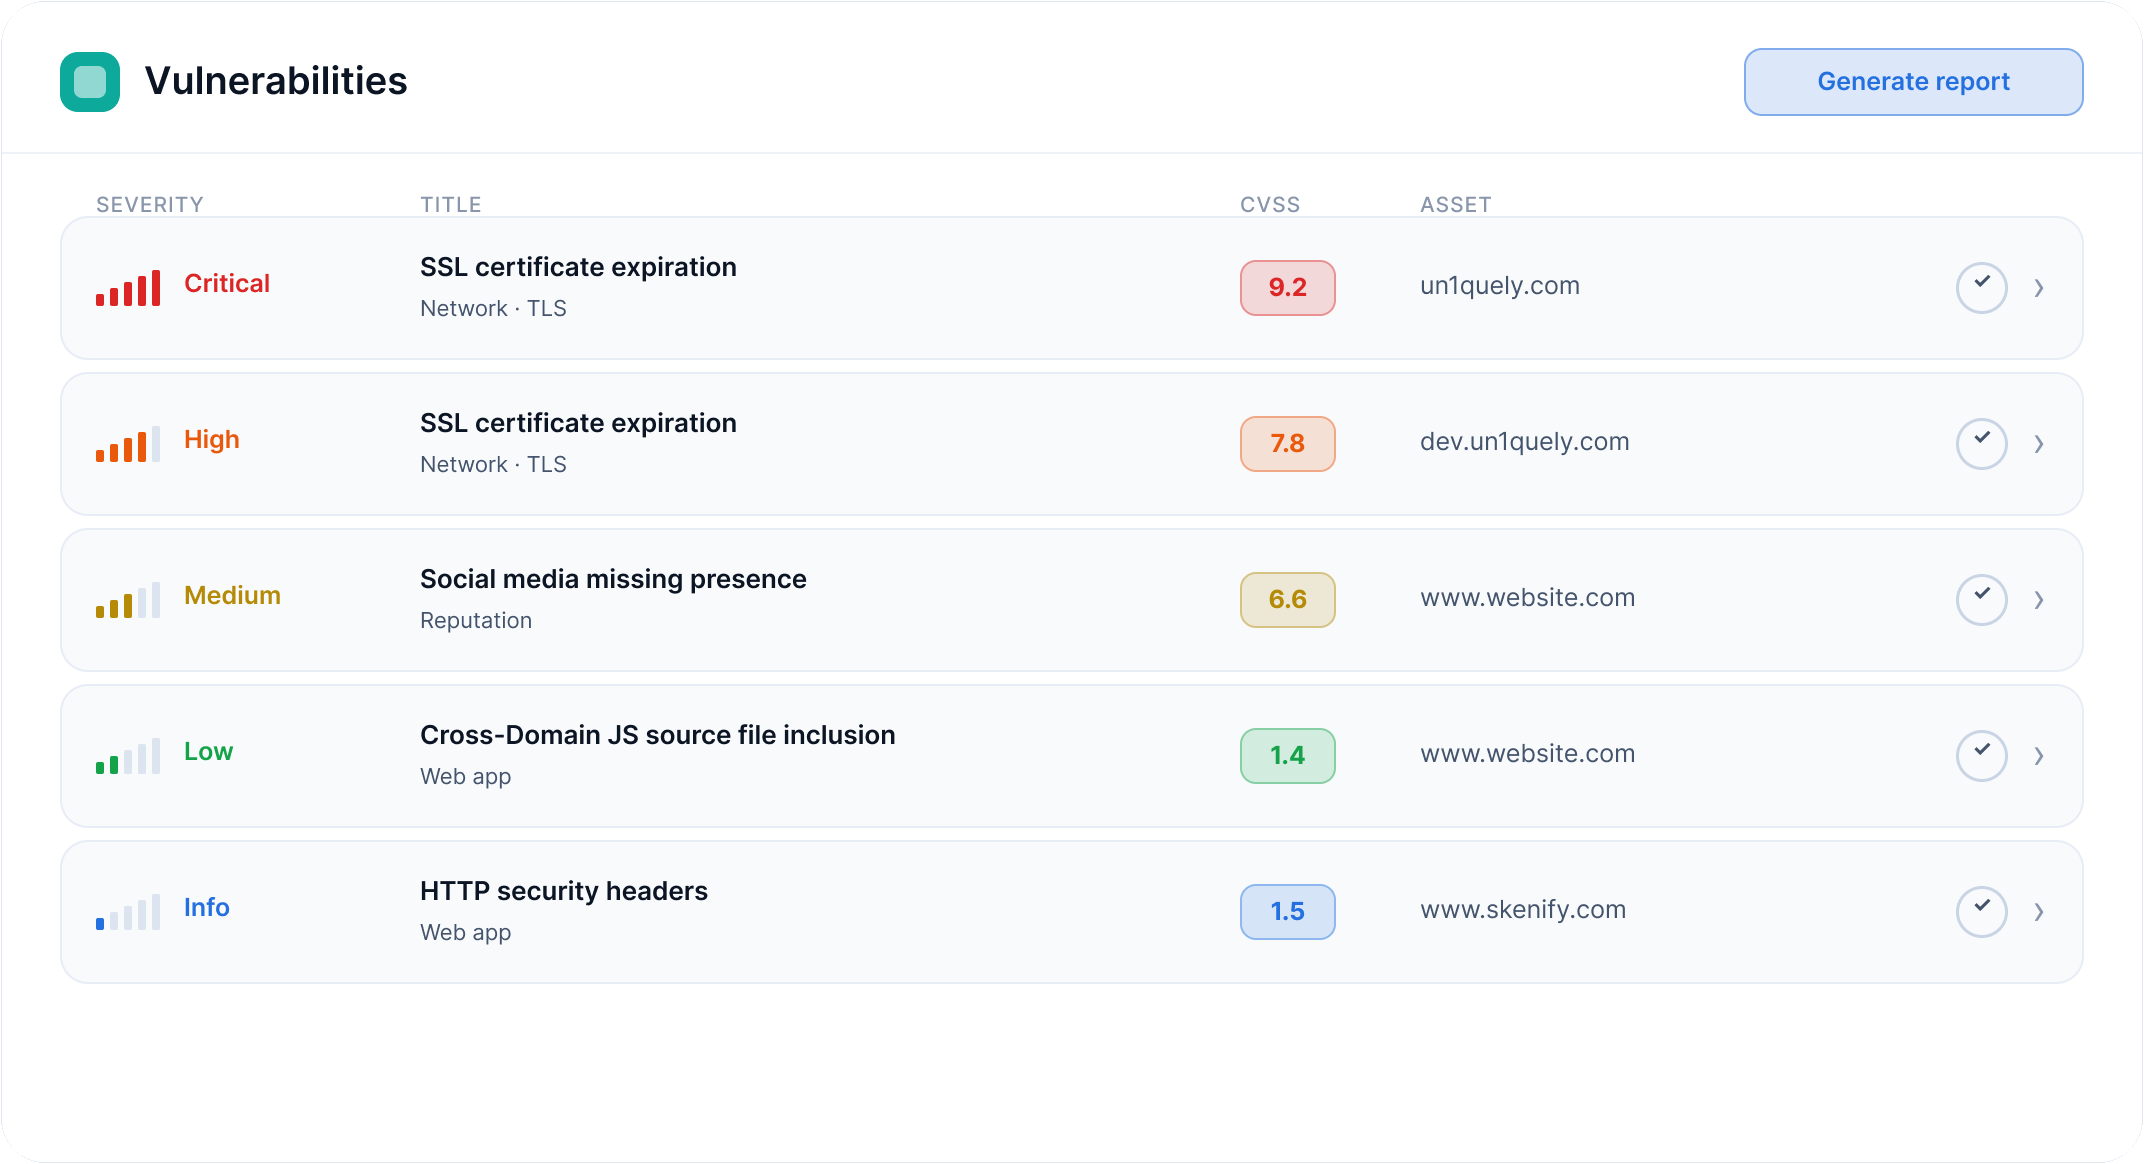
Findings ranked by severity with CVSS, impact and the fix, de-duplicated across hosts.
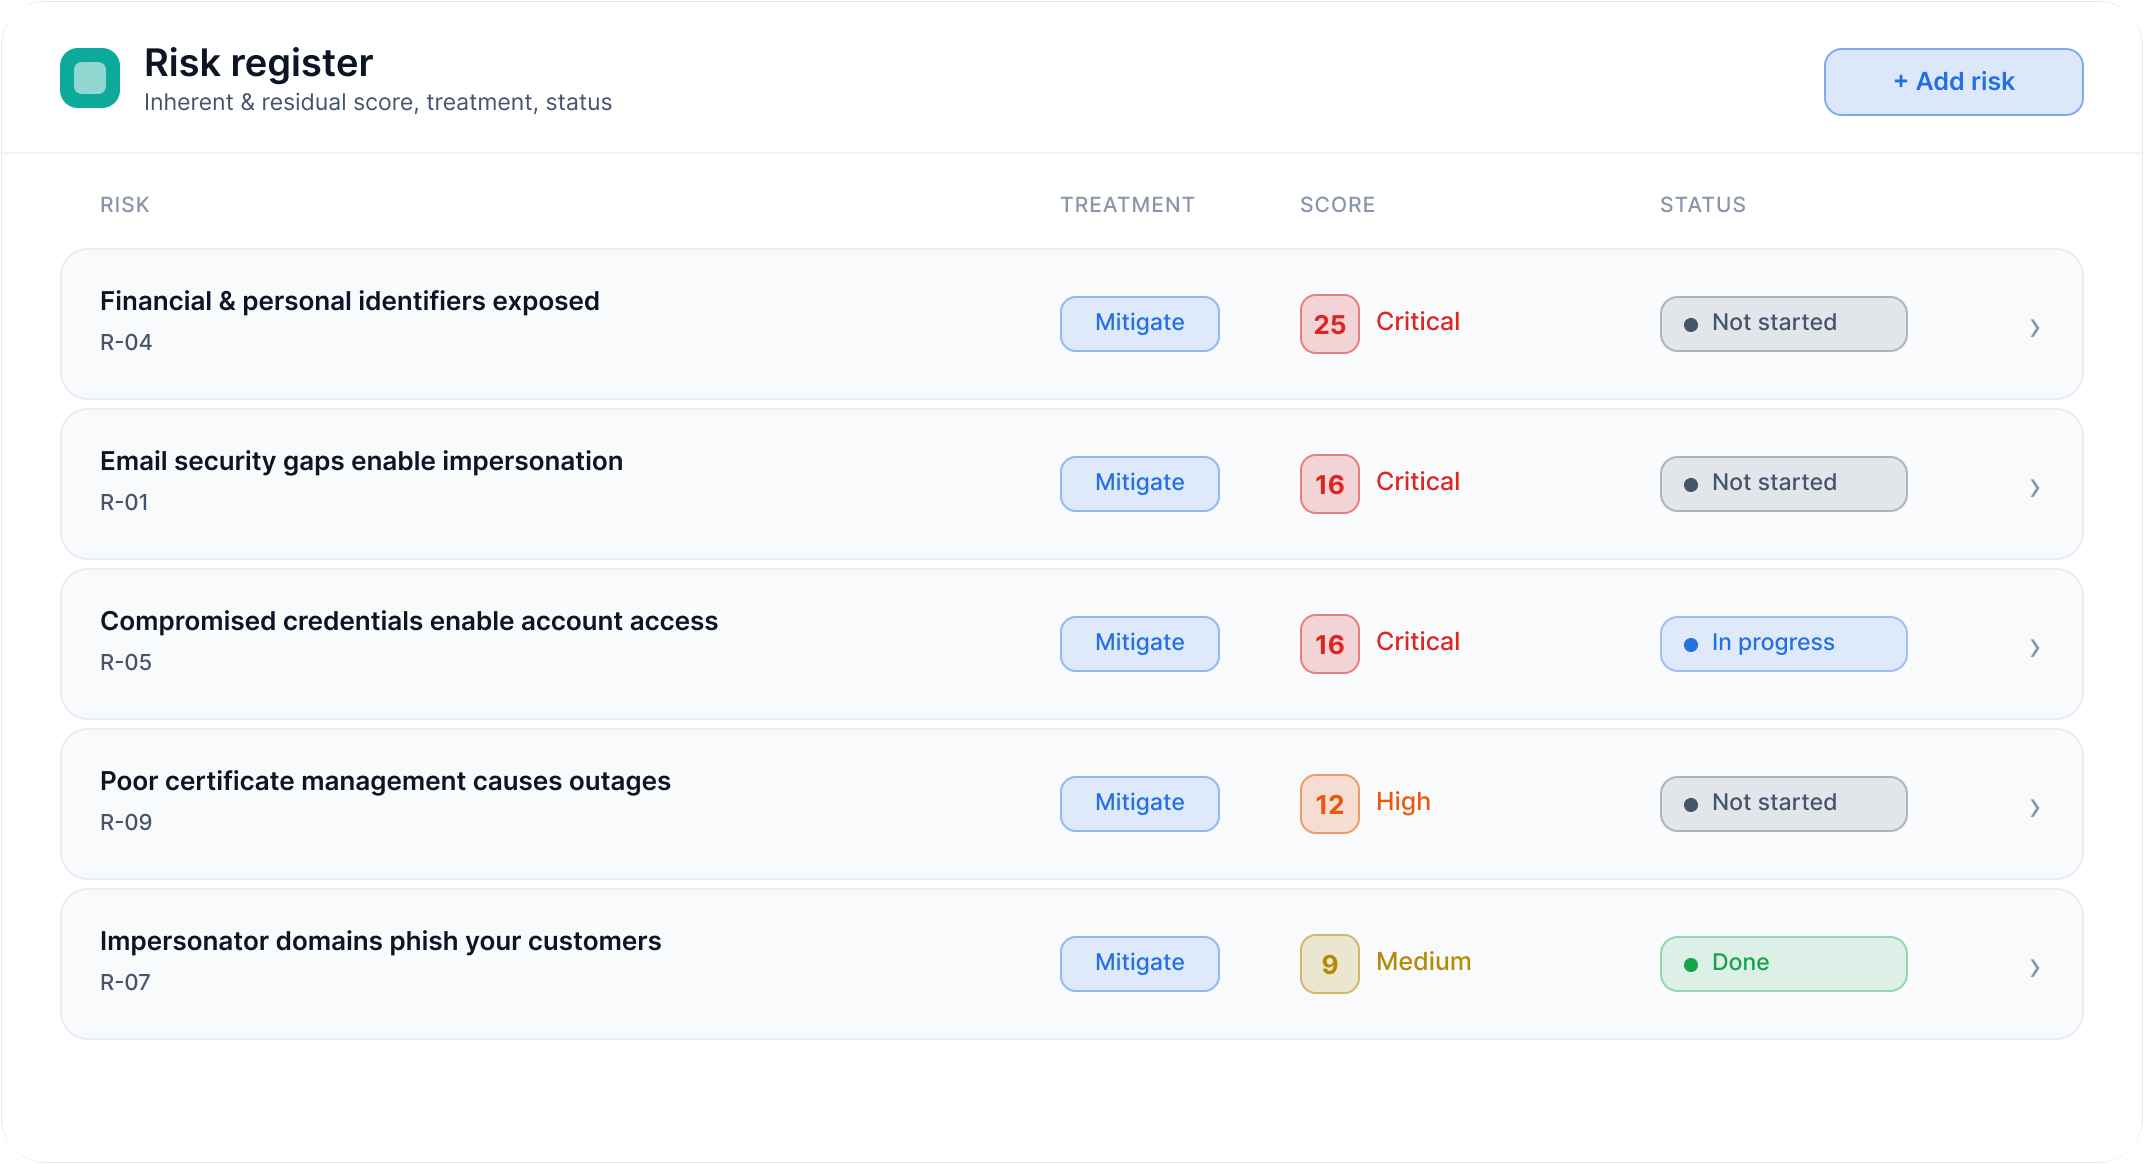
Business-language risk scenarios scored before and after treatment, mapped to ISO 27001 controls.
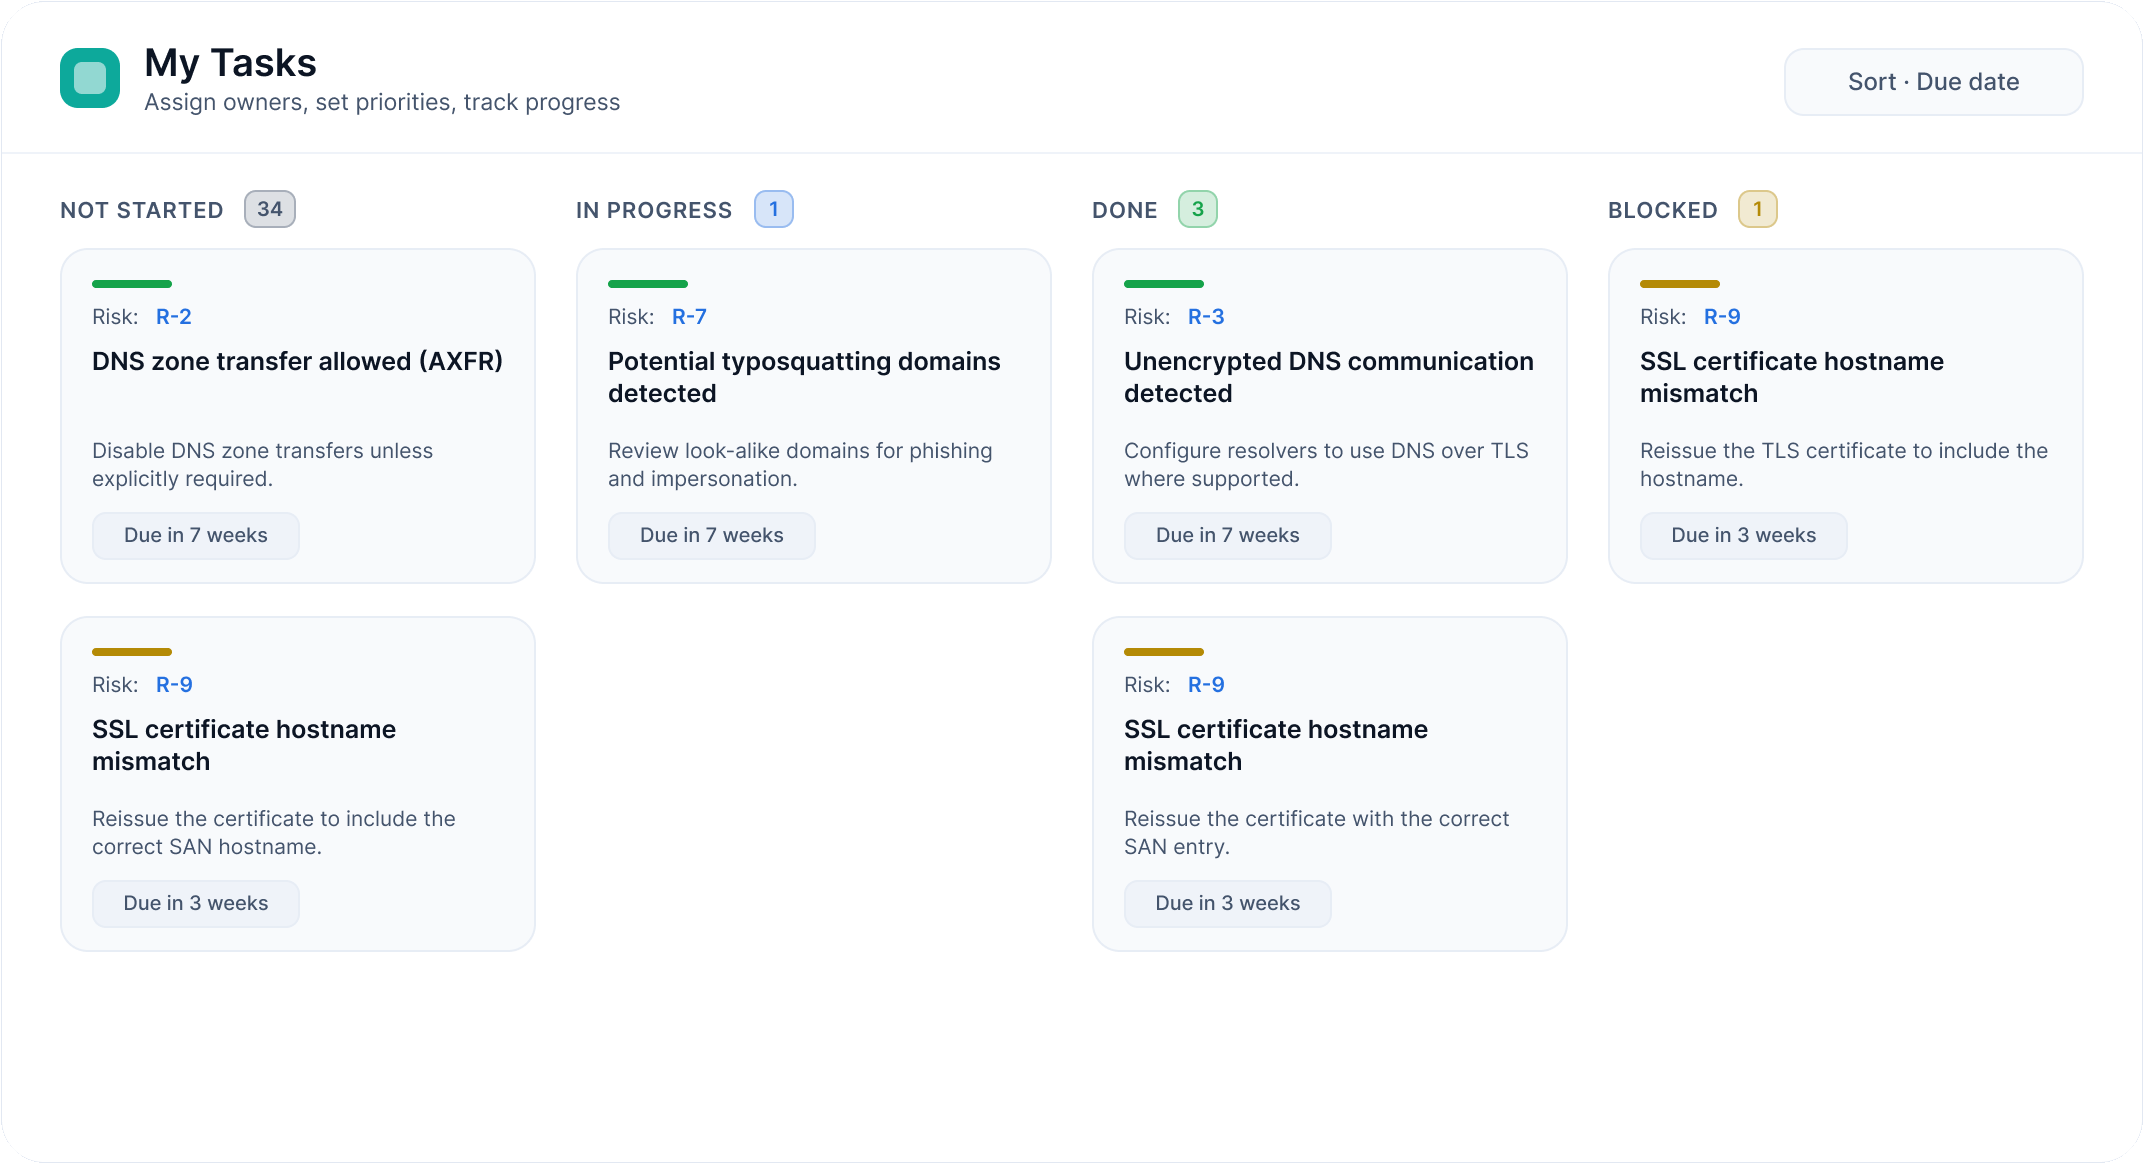
A board that writes itself: one task per finding, with the exact change to make and a deadline from the SLA.
Move your cursor. Every chip is a kind of exposure Skenify finds on real companies.
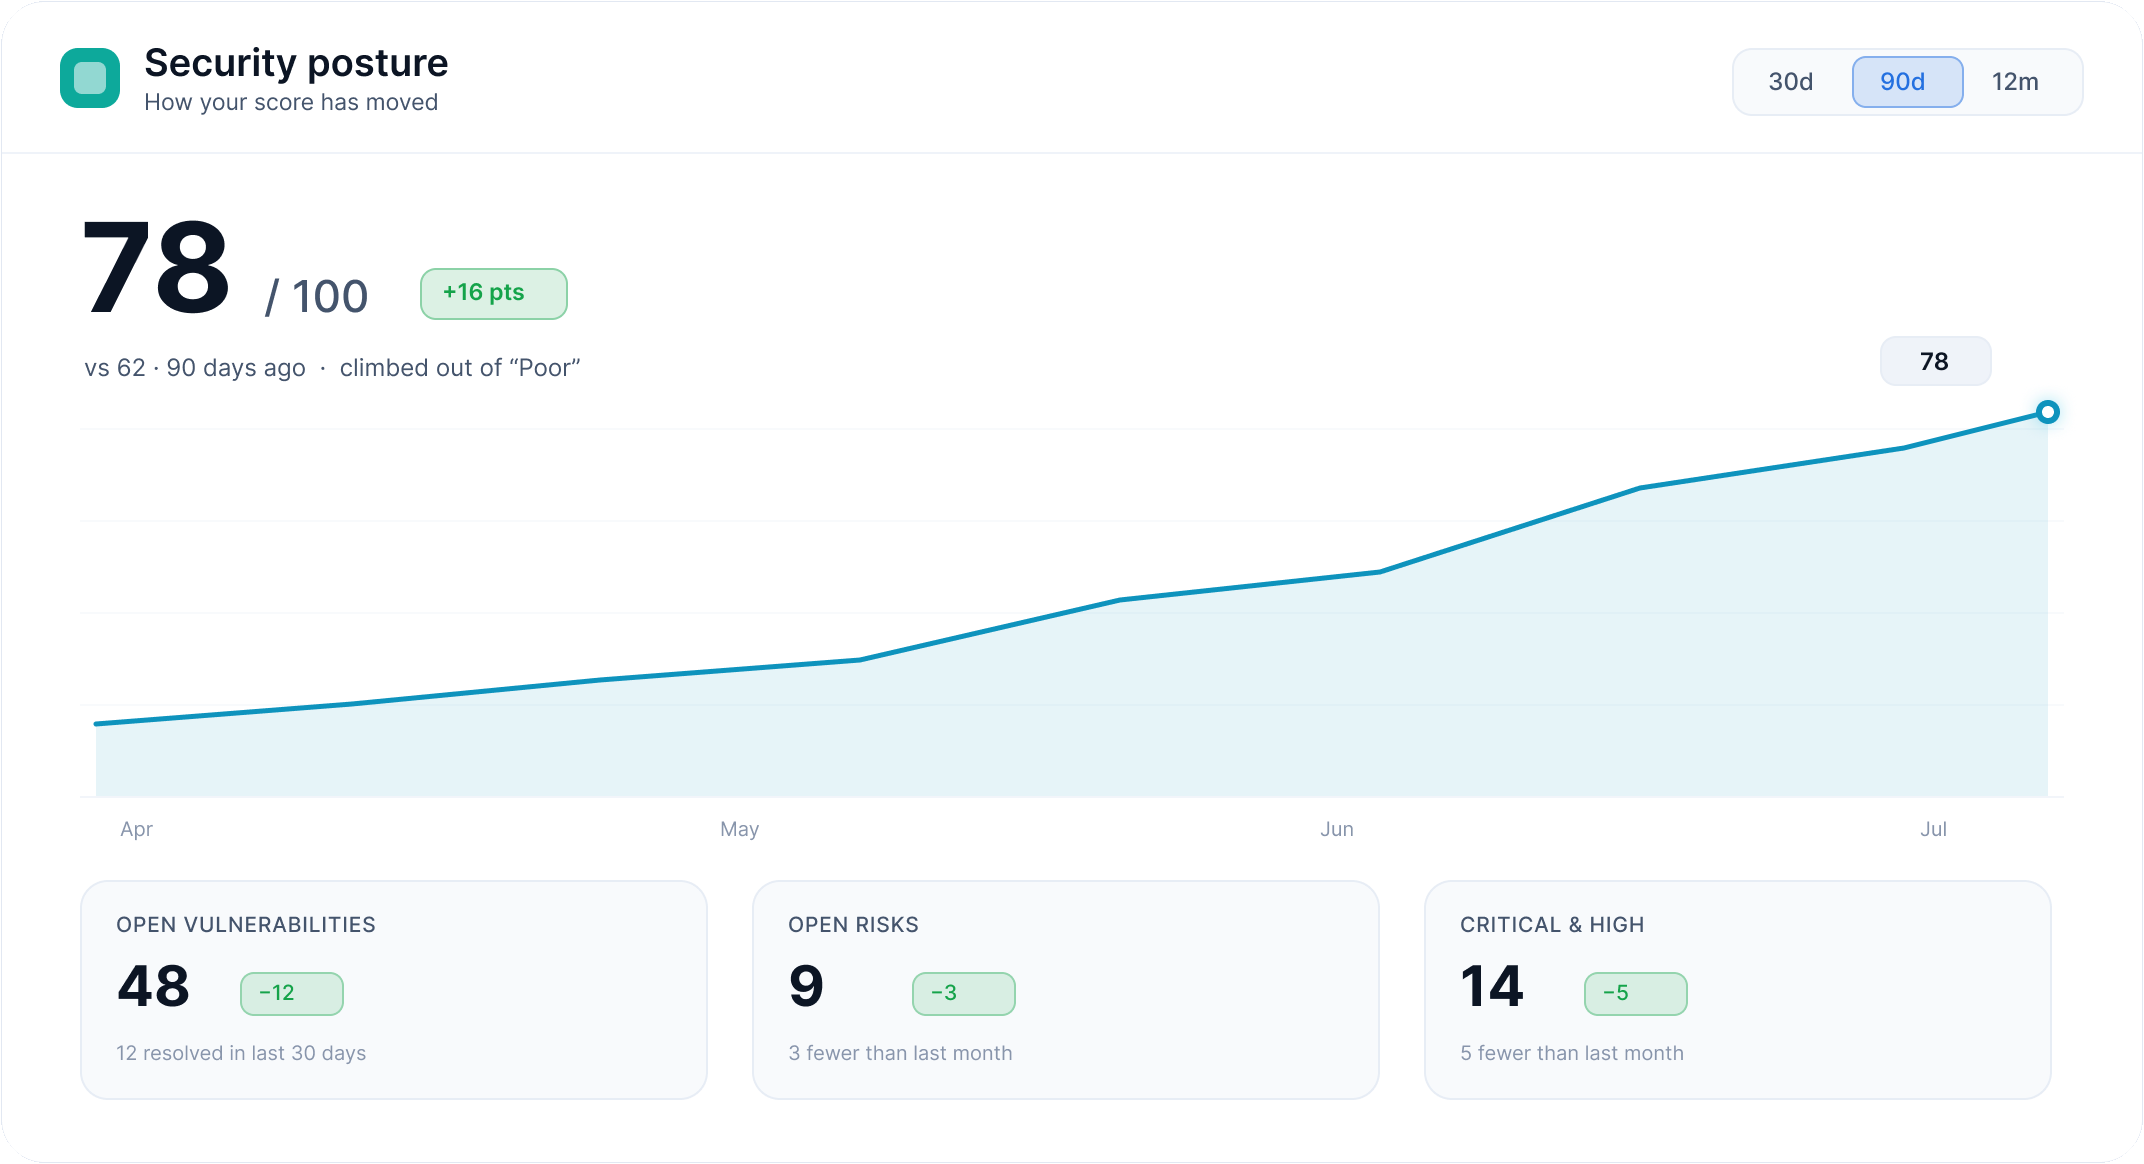
The dashboard opens on a sentence, a score and three things to fix next, ranked by business impact. Each one is already a task with the change spelled out. That is the Monday morning answer, every Monday.
Every risk in the register is linked to the ISO/IEC 27001:2022 controls and clauses it affects. The compliance view shows which of the 93 controls your findings touch and whether each is addressed, needs attention or open. Two reports, a posture report and a compliance impact report, carry a reference and a timestamp, so you can file them for an auditor, a customer or an insurer.
of 93 controls touched
Addressed 6, Needs attention 3, Open 5
“I spent years as a CISO watching companies buy scanners and dashboards and still fail to answer one question: what do we fix first. Skenify is the answer we wished we had. Discovery, testing, scoring and the task list in one place, priced for companies that don't have a security team, or have a team that is at capacity.”
Branko Džakula, founder and CEO
Co-founder of Secfix. Guided more than 100 companies through ISO 27001, NIS2 and DORA.
Discovery, scanning, risk register, task board and compliance reports. One flat rate, unlimited team members, billed annually. Monthly at €599. Seven days free to see your own numbers first.
See pricingPoint-solution estimate: a scanner, a vendor risk tool, a GRC tool and one pentest a year at list prices.
Seven days, no card. We approve requests within 24 hours and findings land about fifteen minutes after you connect.